vCISO
vCISO, your company’s virtual CISO
Virtual Chief Information Security Officer for your company. Strategic information security leadership without the cost of a full-time executive.
Ecosystem connection: SinapseTechLearn more
Service portfolio
GRCtech and Cortex deliver capabilities in governance, risk and AI. Our specialized services help your organization turn those capabilities into practice, method and results.
Our DNA
At SinapseTech, we understand that security and privacy go far beyond meeting regulations. Our integrated approach combines cutting-edge technology, specialized knowledge and proven methodologies to create a complete protection ecosystem.
Advanced protection against digital threats with continuous monitoring and incident response.
Support for meeting data protection legislation through continuous privacy program management.
Robust risk management frameworks aligned with international standards.
Responsible enterprise AI with centralized governance and Shadow AI prevention.
Adherence to NIST, ISO 27000, CIS Controls, LGPD, GDPR and other regulations.
Product and method
Our platforms are the focus. GRCtech and Cortex deliver governance, visibility and applied intelligence. Specialized services help your organization absorb knowledge, interpret context and develop a method to put those capabilities into practice.
GRCtech and Cortex provide continuous controls, organized evidence, executive visibility and applied intelligence.
Multidisciplinary specialists interpret data, contextualize risks, structure a method and guide decisions so the platform’s capabilities translate into practice.
Technology and method help the organization develop its own maturity, accelerate the path to results and operate with growing autonomy.
Technology working in the background. People interpreting the context.
Service portfolio
Nine services to develop maturity in security, privacy and governance. They address standalone needs and help activate the value of the ecosystem platforms.
Virtual Chief Information Security Officer for your company. Strategic information security leadership without the cost of a full-time executive.
Data protection officer as a service. Specialized professionals who act as your DPO, supporting continuous compliance with LGPD and other legislation.
Responsible AI deployment with the Cortex platform. Centralized governance, Shadow AI prevention and intelligent process automation to boost your organization's productivity.
Implementation of governance frameworks aligned with NIST, CIS Controls and ISO 27000, with policies, processes and metrics for efficient risk management.
Support for meeting LGPD, GDPR and other regulations. Automate compliance processes and maintain continuous visibility into the regulatory requirements applicable to your business.
Complete privacy program management, from personal data mapping to implementing controls and processes to fulfill data subject rights.
Detailed security and privacy maturity assessments, identifying gaps, vulnerabilities and improvement opportunities with prioritized action plans.
Advanced protection of your digital infrastructure with continuous monitoring, incident response, penetration testing and vulnerability management.
Customized training programs that transform employees into active security and privacy defenders, creating a resilient organizational culture.
Ecosystem
Our services work independently and also help activate the platforms in the SinapseTech ecosystem.
GRCtech
Governance, risk and compliance in a single source of truth. Our governance, audit, privacy and compliance services structure the method that turns GRCtech’s capabilities into practice.
Discover GRCtechCortex
Artificial intelligence governance and security. Our enterprise AI service deploys Cortex with policies, controls and measures to address Shadow AI.
Discover CortexHow we work
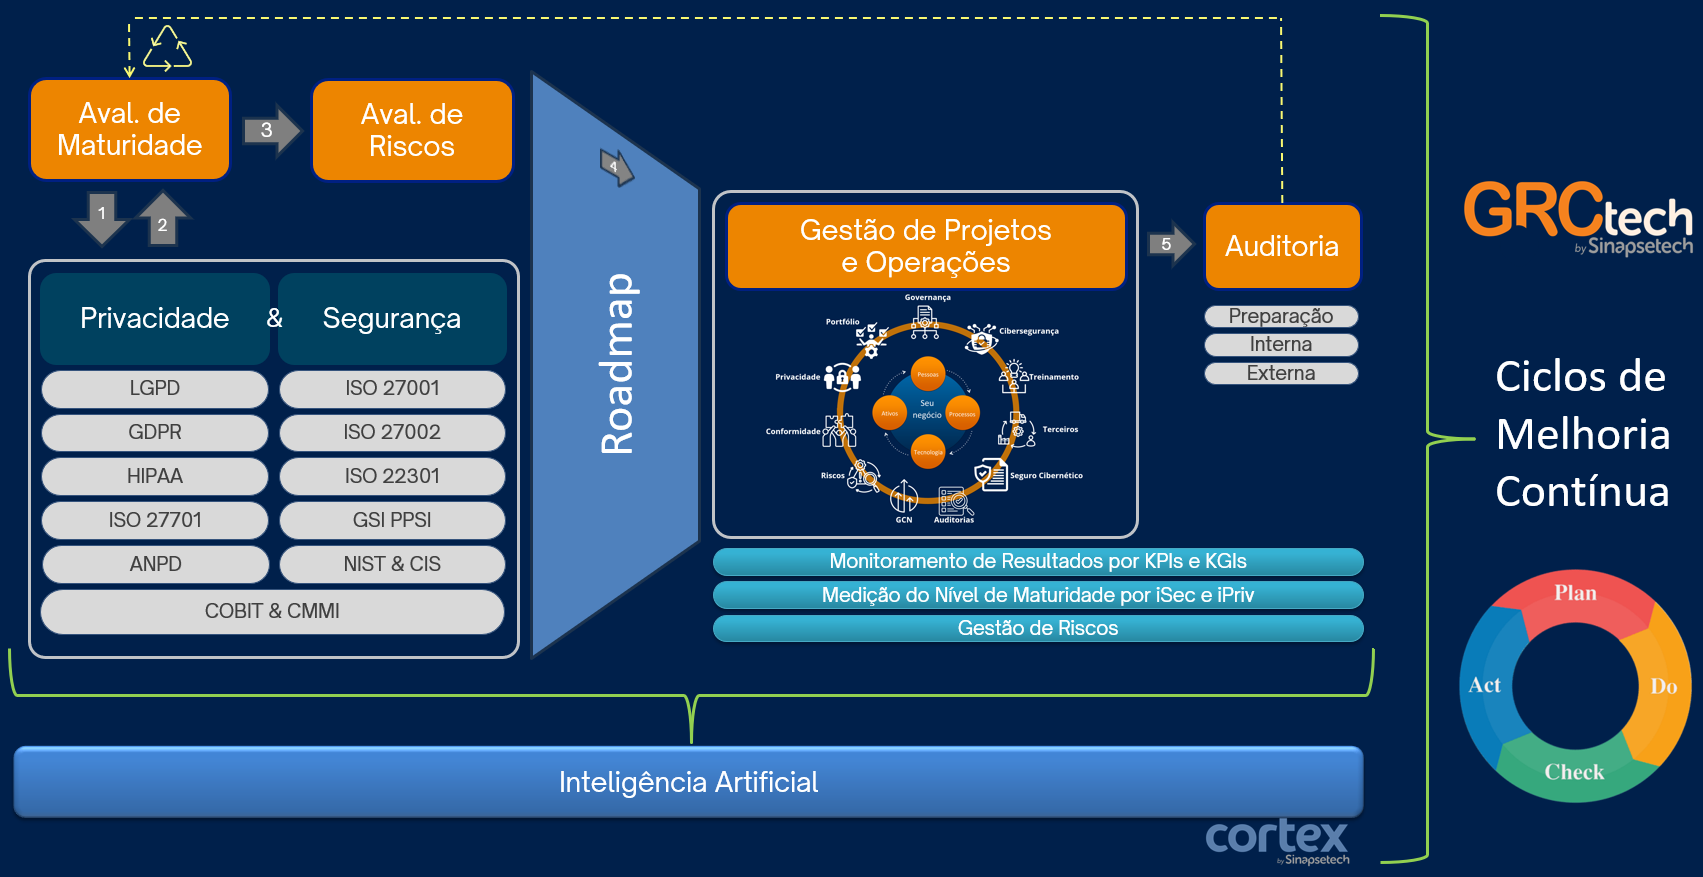
Our approach is based on the PDCA cycle of planning, doing, checking and acting, guiding continuous improvement in security and privacy processes. We plan, execute, verify and adjust each step to achieve sustainable and measurable results.

From maturity assessment to the roadmap, execution and audit: a cycle of continuous improvement.
Original diagram in Portuguese.The diagram starts with a maturity assessment, connected in both directions to privacy and security. Under privacy, the artwork lists LGPD, GDPR, HIPAA, ISO 27701 and ANPD; under security, ISO 27001, ISO 27002, ISO 22301, GSI PPSI and NIST & CIS. COBIT & CMMI appear as shared references. The maturity assessment leads to a risk assessment, a roadmap and project and operations management. At this core, people, assets, processes and technology connect with portfolio, governance, cybersecurity, training, third parties, cyber insurance, audits, business continuity management, risks, compliance and privacy. Audit includes preparation, internal and external audits, with a return to the maturity assessment. Cross-cutting monitoring brings together results monitoring through KPIs and KGIs, maturity measurement through iSec and iPriv, and risk management. An artificial intelligence foundation identified by Cortex supports the journey; GRCtech identifies the continuous improvement cycles. On the right, the PDCA cycle shows Plan, Do, Check and Act. The standards and frameworks mentioned are diagram references, not certification claims.
Assess maturity and risks to define scope, priorities, criteria and a roadmap.
Implement controls and processes through project and operations management.
Monitor results, evidence and indicators, measure maturity and perform audits.
Adjust priorities, correct deviations and restart the assessment cycle to guide continuous progress.
Building trust
Specialized knowledge, technology and method in trusted relationships with our clients.

SinapseTech was the best solution for supporting the Delly's Privacy and Security Program Management. In addition to technical knowledge and availability, the team uses tools that maintain assertive control of risks and action plans. The training part is excellent. We are very satisfied with the consulting.
The partnership with SinapseTech was fundamental for our company to effectively master the implementation and maintenance of the necessary controls involving the correct handling of personal data. I highlight the experience and competence of this team of professionals dedicated to adapting our processes to the General Data Protection Law.
Frequently asked questions
No. SinapseTech services work independently to address security, privacy and governance needs. They can also help activate the GRCtech and Cortex platforms.
The vCISO provides strategic information security leadership. DPO as a Service provides specialized professionals to act as the data protection officer, supporting continuous compliance with LGPD and other legislation.
The cycle brings together Plan, Do, Check and Act: assess maturity and risks to plan, implement controls and processes, monitor results and evidence, and adjust the approach. The diagram presents this work as a cycle of continuous improvement.
Governance, audit, privacy and compliance services structure the method for applying GRCtech’s capabilities. The enterprise AI service deploys Cortex with policies, controls and measures to address Shadow AI. In both paths, specialists help interpret data and contextualize risks to guide decisions.
Contact our specialists and discover how our integrated solutions can protect your data, optimize processes and drive your company's growth.
Contact us